Security Threat Assessment
Threat Assessment provides the first analytical input into the security risk process by defining threat actors, intent, capability, and operating conditions within a defined Assessment Area and Assessment Period. The process is executed by building an Area Threat Context (ATC), identifying assets and exposure,…
- Delivery
- Online
- Duration
- Self-paced online
- Assessment
- Scenario-based assessment
- Course application
- Apply for this course
What you will learn and demonstrate.
Course Overview
Threat Assessment provides the first analytical input into the security risk process by defining threat actors, intent, capability, and operating conditions within a defined Assessment Area and Assessment Period.
The process is executed by building an Area Threat Context (ATC), identifying assets and exposure, and assessing threats using structured matrices (Layer 1) supported by verified information and analytical judgement. Threat ratings are assigned with confidence levels and validated through structured consistency checks.
Operational Threat Scenarios (Layer 2) are developed to define how threats may materialize, including actor, motive, method, and enabling conditions. These scenarios directly support operational planning, protection design, and risk assessment.
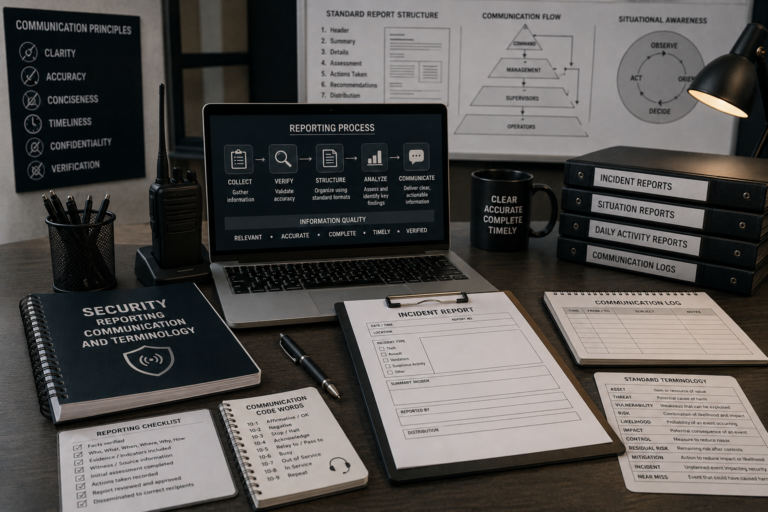
All inputs are processed through the Security Information Cycle (SIC) and recorded in an Evidence Log, ensuring traceability, accuracy, and auditability. Analytical outputs must distinguish between Known information and Assessed judgement and must remain evidence-based.
The final output is a Design Basis Threat (DBT) derived from ATC, Layer 1, and Layer 2 outputs. The DBT defines the adversary profile that security measures must address and supports SMART-based risk assessment, Operational Security Planning (OSP), and Security & Crisis Management (SSCM).
Capability Development Chain
Assessment Area → ATC → Asset Exposure → Threat Assessment (L1) → Operational Threat Scenarios (L2) → DBT → SMART Input
Participants shall
define scope and timeframe
build Area Threat Context
identify assets and exposure
assess threats using structured matrices
develop operational scenarios
verify analytical integrity
produce DBT
ensure traceability to Evidence Log
Key Concepts
- Define and scope the Assessment Area and Assessment Period with justified assumptions, boundaries, and ownership
- Build the Area Threat Context (ATC) using PESTLE+ and STRIPE to identify drivers of insecurity and threat relevance
- Apply the Security Information Cycle (SIC) to ensure ATC inputs are accurate, relevant, and traceable
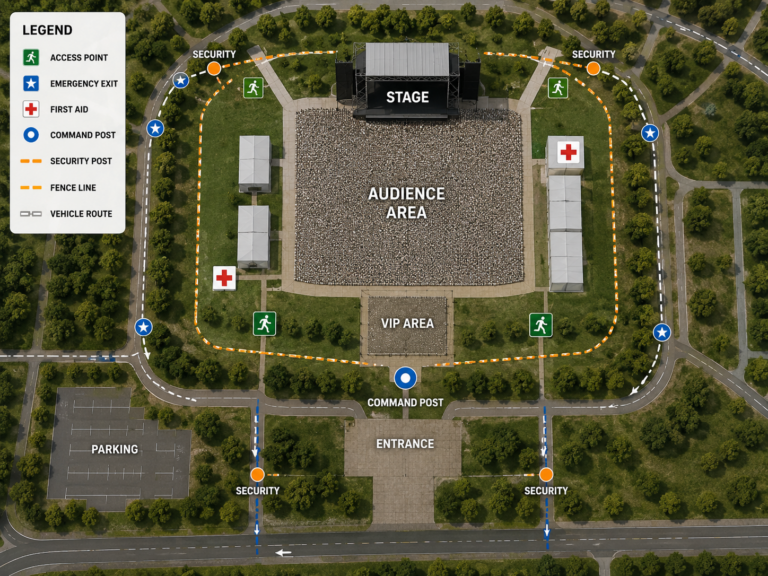
- Identify assets, activities, objectives, and exposure patterns within the Assessment Area
- Distinguish Threat Assessment (Layer 1) from Operational Threat Scenarios (Layer 2) and maintain separation of outputs
- Assess threats using structured matrices by evaluating intent, capability, and operating conditions
- Assign threat ratings using qualitative scales, confidence levels, and evidence-based justification
- Apply SIC to strengthen threat ratings and scenario development through verified and traceable information
- Conduct validity checks to identify inconsistencies, bias, and analytical drift across ATC, Layer 1, and Layer 2
- Develop Operational Threat Scenarios (Layer 2) defining actor, motive, method, and enabling conditions
- Ensure all analytical outputs are supported by traceable evidence recorded in the Evidence Log
- Define the Design Basis Threat (DBT) derived from ATC, Layer 1, and Layer 2 outputs without influencing threat ratings
- Apply DBT to guide protection design, including deterrence, detection, delay, and denial requirements
- Maintain traceability chains linking ATC → Layer 1 → Layer 2 → DBT → Evidence Log
- Integrate threat outputs into SMART to support Risk Assessment, OSP, and SSCM
- Produce structured, auditable, and decision-ready threat assessment outputs
MODULE 1: ASSESSMENT AREA & PERIOD+
Purpose
Define analytical boundaries and validity of the assessment.
Learning Outcomes
define Assessment Area based on threat homogeneity
define Assessment Period linked to operational context
verify alignment between area, timeframe, and analysis
identify risks of over- and under-scoping
justify assumptions using evidence
Key Exercises
define Assessment Area and justify boundary
assign Assessment Period and document assumptions
identify impact of incorrect scoping
MODULE 2: AREA THREAT CONTEXT (ATC)+
Purpose
Establish evidence-based understanding of insecurity drivers.
Learning Outcomes
identify political, economic, social, environmental, infrastructure, security forces, and threat actor drivers
structure ATC using PESTLE+ and STRIPE logic
determine relevance of contextual factors to security
link ATC findings to potential threats
assign confidence levels to ATC inputs
verify traceability through Evidence Log
Key Exercises
build ATC narrative using structured inputs
identify drivers of insecurity
assign confidence levels and justify sources
MODULE 3: ASSET & EXPOSURE ANALYSIS+
Purpose
Define asset exposure to threat environment.
Learning Outcomes
identify assets, activities, and operational objectives
determine exposure through activity, method, time, and location
differentiate general and specific exposure
link assets to threat relevance
assign ownership and accountability
Key Exercises
map assets and exposure patterns
identify exposure drivers
classify assets by exposure level
MODULE 4: THREAT ASSESSMENT (LAYER 1)+
Purpose
Assess threat actors using structured and traceable methodology.
Learning Outcomes
identify relevant threat actors
classify actors using defined taxonomy
assess intent, capability, and operating conditions
differentiate Known and Assessed threats
apply structured Threat Matrix
assign confidence levels
conduct validity check to identify inconsistencies
justify threat ratings using evidence
Key Exercises
complete Threat Matrix
assign ratings with justification
conduct validity check and correct inconsistencies
MODULE 5: OPERATIONAL THREAT SCENARIOS (LAYER 2)+
Purpose
Define realistic, decision-relevant threat scenarios.
Learning Outcomes
construct scenarios describing actor, motive, method, and conditions
link scenarios to Assessment Area and timeframe
define how threats may materialize
ensure scenarios are evidence-based
assign confidence levels
verify traceability to Layer 1 and ATC
Key Exercises
build operational threat scenarios
link scenarios to threat actors and context
validate scenario realism and relevance
MODULE 6: SECURITY INFORMATION CYCLE (SIC)+
Purpose
Ensure all threat assessment inputs are accurate, relevant, and traceable.
Learning Outcomes
determine Information Requirements using 5W+H and indicators
acquire information from authorized sources
examine reliability, relevance, and timeliness
collate information into structured format
analyse information to support threat assessment
disseminate outputs to stakeholders
differentiate raw and processed information
assign confidence levels and justify
maintain Evidence Log linking all inputs
Key Exercises
build Information Requirements
conduct source selection and justification
apply Group A and Group B examination
structure and analyse collected information
build Evidence Log
MODULE 7: VALIDITY CHECK & ANALYTICAL CONTROL+
Purpose
Ensure integrity and consistency of threat assessment.
Learning Outcomes
identify anomalies and inconsistencies in threat ratings
verify alignment between ATC, Layer 1, and Layer 2
detect bias and analytical drift
apply structured validity check
justify corrections using evidence
Key Exercises
conduct validity check on Threat Matrix
identify inconsistencies and correct ratings
validate alignment across outputs
MODULE 8: DESIGN BASIS THREAT (DBT)+
Purpose
Define threat benchmark for security design.
Learning Outcomes
derive DBT from ATC, Layer 1, and Layer 2
define adversaries, methods, and conditions
ensure DBT is evidence-based
verify DBT is not influencing threat ratings
align DBT with protection requirements
Key Exercises
construct DBT profile
justify DBT components
verify separation from threat rating process
MODULE 9: TRACEABILITY & EVIDENCE LOG+
Purpose
Ensure all analytical outputs are auditable and defensible.
Learning Outcomes
record all sources, timestamps, and references
link Evidence Log to ATC, Layer 1, and Layer 2
verify traceability chain
assign confidence levels
identify gaps in information
Key Exercises
build Evidence Log
link evidence to threat ratings and scenarios
identify missing or weak evidence
MODULE 10: INTEGRATION INTO SMART+
Purpose
Convert threat assessment outputs into risk inputs.
Learning Outcomes
link threat outputs to vulnerability and risk
support development of Operational Risk Scenarios
provide inputs for Risk Assessment (Likelihood and Impact)
support OSP and SSCM
verify alignment with SMART chain
Key Exercises
map threat outputs into SMART
define link between threat and risk
prepare inputs for risk assessment
MODULE 11: ANALYTICAL INTEGRITY+
Purpose
Prevent manipulation and ensure objective assessment.
Learning Outcomes
identify attempts to bias or influence outcomes
prevent retrofitting of analysis
verify evidence-based reasoning
maintain analytical independence
justify all outputs
Key Exercises
identify manipulated assessments
correct biased inputs
rebuild defensible assessment
MODULE 12: FINAL OPERATIONAL SCENARIO+
Purpose
Validate full threat assessment capability.
Scenario Conditions
incomplete information
conflicting inputs
time pressure
evolving threat indicators
Learning Outcomes
define Assessment Area and Period
build ATC
assess threats (Layer 1)
develop scenarios (Layer 2)
apply SIC
conduct validity check
produce DBT
ensure traceability
Key Exercises
execute full threat assessment process
justify all outputs
defend assessment
Assessment Requirements
Assessment Area & Period definition
ATC narrative
Threat Matrix (Layer 1)
Operational Threat Scenarios (Layer 2)
Evidence Log
Dbt
SMART integration outputs
Need help choosing the right training?
Tell us the role, capability, or operational requirement you need to address.
Apply for this course.
Submit your course selection and applicant details. Supporting documents are requested separately after review.
Need this capability across an organization or public-service unit?
We adapt course scope, scenarios, delivery, and assessment to your staff, mandate, and operating environment.